Last year, Chrome announced that it was making a change to default cookies to SameSite:Lax if there is no SameSite setting explicitly set. I wrote about this change last year (https://www.jardinesoftware.net/2019/10/28/samesite-by-default-in-2020/). This change could have an impact on some sites, so it is important that you test this out. The changes are supposed to start rolling out in February (this month). The linked post shows how to force these defaults in both FireFox and Chrome. In … [Read more...] about Chrome is making some changes.. are you ready?
General
Investing in People for Better Application Security
Application security, like any facet of security, is a complex challenge with a mountain of solutions. Of course, no one solution is complete. Even throwing multiple solutions will never get 100% coverage. The push today is around devsecops, or pushing left in the SDLC. I am seeing more solutions recommending also pushing right in the SDLC. I feel like we are stuck at this crossroad where the arrow points both ways. The good news is that none of these recommendations are wrong. We do need to … [Read more...] about Investing in People for Better Application Security
Interesting Browser Difference
Update 8/16/19 - It appears that not long after I published this, Chrome sent an update that now mimics FireFox. In Chrome you now get a new tab that has a URL of "about:blank#blocked". When working on a recent test I noticed something pretty interesting when I had found what I thought was a Cross-Site Scripting vulnerability. I have posted previously on the ability to execute XSS when you control the HREF attribute of a link tag. This is done by setting a url to javascript:alert(9);. This … [Read more...] about Interesting Browser Difference
XSS in Script Tag
Cross-site scripting is a pretty common vulnerability, even with many of the new advances in UI frameworks. One of the first things we mention when discussing the vulnerability is to understand the context. Is it HTML, Attribute, JavaScript, etc.? This understanding helps us better understand the types of characters that can be used to expose the vulnerability. In this post, I want to take a quick look at placing data within a <script> tag. In particular, I want to look at how embedded … [Read more...] about XSS in Script Tag
Apple Mail: Highlighting External Email Addresses
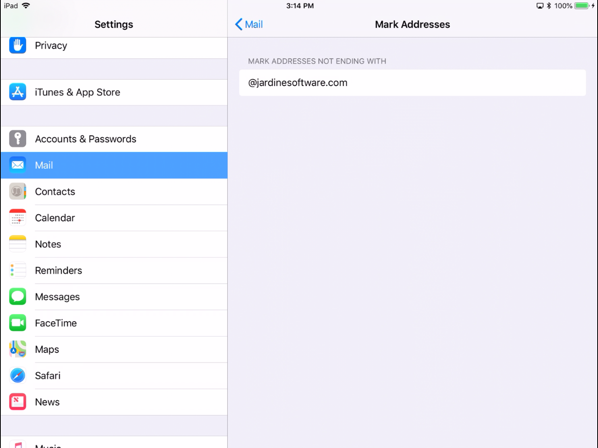
A simple error to make when sending an email with sensitive data is to send it to the wrong email address. Imagine you are sending some information to Dave down in accounting. When you fill out the email you start typing Dave and the auto-complete pops up and you select the first one (out of habit). You think you have selected the right Dave, but what if you didn't? How would you know that you were about to send potentially sensitive information outside of the organization? Apple Mail and iOS … [Read more...] about Apple Mail: Highlighting External Email Addresses
Checking npm packages using npm-audit
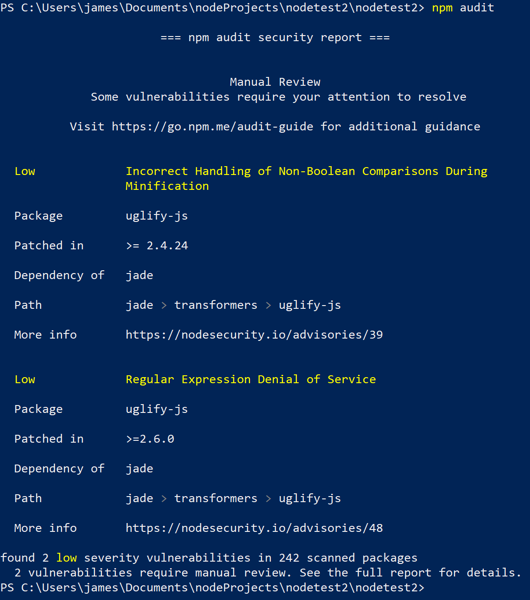
Our applications rely more and more on external packages to enable quick deployment and ease of development. While these packages help reduce the code we have to write ourselves, it still may present risk to our application. If you are building Nodejs applications, you are probably using npm to manage your packages. For those that don't know, npm is the node package manager. It is a direct source to quickly include functionality within your application. For example, say you want to hash your … [Read more...] about Checking npm packages using npm-audit