When it comes to application vulnerabilities, there are 2 common groups we might view them: Technical Debt and New Development. I break these down because the way in which we address vulnerabilities is fundamentally different. Something that might not be exploitable receives a very low priority when it is technical debt. However, during new development, it can be addressed with little cost. Much of this comes down to if soemthing is syntactically insecure vs. actually vulnerable. Let’s look at … [Read more...] about Technical Debt vs. New Dev
General
The risk of Spell Checking
Did you know that input fields on a web form support spell checking by default in many web browsers? This is a feature of the browser that can help catch errors early for the end user. Recently, some testers found that some data may be leaked during the spell checking function to 3rd parties. Here is a reference article describing this: https://www.darkreading.com/application-security/spellchecking-google-chrome-microsoft-edge-browsers-leaks-passwords The first point to make here is this is … [Read more...] about The risk of Spell Checking
Input validation is less about specific vulnerabilities
Security takes a layered approach to reduce the risk to our organization. Input validation is the perfect example of one of these layers. In most cases, input validation is 1 factor in a multi-pronged approach to protecting against common vulnerabilities. Take any course on secure development and they will, or should, mention input validation as a mitigating control for so many vulnerabilities. You might notice that it always comes with a but. Use input validation, but also use output … [Read more...] about Input validation is less about specific vulnerabilities
Is encoding really encoding if it is escaping?
The title might be confusing, let's see if we can clear it up. I saw an article the other day that was giving a comparison between encoding, encryption and hashing. There was a statement made that basically said: Encoding has no security purpose. I thought this was interesting because when training on security topics we mention encoding for specific use cases. For example, when we discuss Cross-Site Scripting, the answer is output encoding. I want to clarify that I agree with the statement … [Read more...] about Is encoding really encoding if it is escaping?
Log4J – Reflection and Progression
Open any social media platform or pull up any mainstream media and undoubtably, you have seen many posts/articles talking about the log4j vulnerability. If you haven't seen this, here is a quick link to catch up https://snyk.io/blog/log4j-rce-log4shell-vulnerability-cve-2021-4428/. This post is not going to be about log4j, nor is it going to go into any of the details the thousands of others articles out there would go through. Instead, I want to discuss this at a higher level. Log4j is just an … [Read more...] about Log4J – Reflection and Progression
Proxying localhost on FireFox
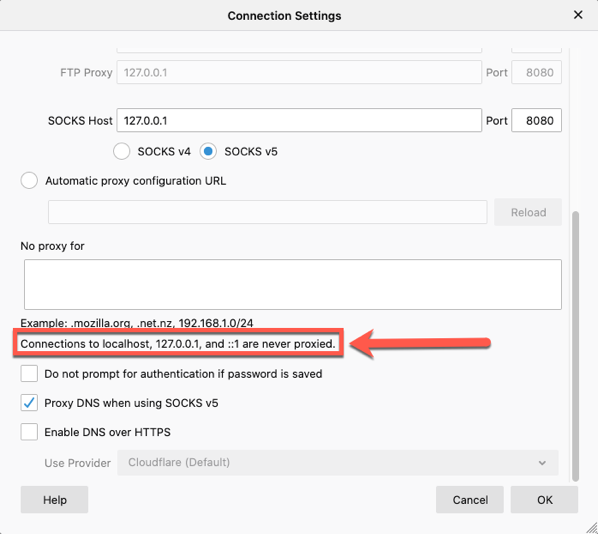
When you think of application security testing, one of the most common tools is a web proxy. Whether it is Burp Suite from Portswigger, ZAP from OWASP, Fiddler, or Charles Proxy, a proxy is heavily used. From time to time, you may find yourself testing a locally running application. Outside of some test labs or local development, this isn't really that common. But if you do find yourself testing a site on localhost, you may run into a roadblock in your browser. If you are using a recent version … [Read more...] about Proxying localhost on FireFox