If an auditor asked you what applications exist on your network, how accurate do you think your answer would be? Do you have a repository or registry of the applications your company maintains? A good application security program starts with knowing what you have. Without this knowledge it is very difficult to understand the risk the applications bring to the company. Depending on the maturity of your application security program, the way that applications are registered can be very … [Read more...] about Application Registry: Knowing Your Assets
General
Does the End of an Iteration Change Your View of Risk?
You have been working hard for the past few weeks or months on the latest round of features for your flagship product. You are excited. The team is excited. Then a security test identifies a vulnerability. Balloons deflate and everyone starts to scramble. Take a breath. Not all vulnerabilities are created equal and the risk that each presents is vastly different. The organization should already have a process for triaging security findings. That process should be assessing the risk of the … [Read more...] about Does the End of an Iteration Change Your View of Risk?
Password Storage Overview
Start reading the news and you are bound to read about another data breach involving user credentials. Whether you get any details about how the passwords (that were stolen) were stored, we can assume that in many of these cases that they were not well protected. Maybe they were stored in clear text (no, it can't be true), or use weak hashes. Passwords hold the key to our access to most applications. What are you doing to help protect them? First, lets just start with recommending that the … [Read more...] about Password Storage Overview
Untrusted Data: Quick Overview
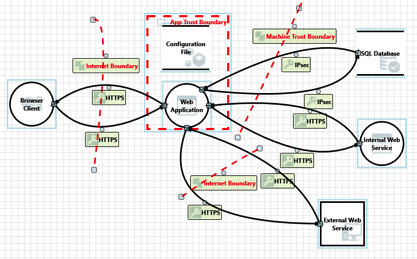
In the application security community it is common to talk about untrusted data. Talk about any type of injection attack (SQLi, XSS, XXE, etc) and one of the first terms mentions is untrusted data. In some cases it is also known as user data. While we hear the phrase all the time, are we sure everyone understands what it means? What is untrusted data? It is important that anyone associated with creating and testing applications understand the concept of untrusted data. Unfortunately, it can … [Read more...] about Untrusted Data: Quick Overview
Insufficient Session Expiration: Testing
Insufficient Session Timeout is a security flaw that can mean a few different things. One common finding for this is that the session timeout is set too long. For example, the session is valid after an hour of being idle. Another common finding is when the session is not properly terminated after the user uses the logout/sign out feature. In this post we will cover these two test cases and how to test for them. A.K.A Insufficient Logout Insecure Logout Insufficient Session … [Read more...] about Insufficient Session Expiration: Testing
HTTP Strict Transport Security (HSTS): Overview
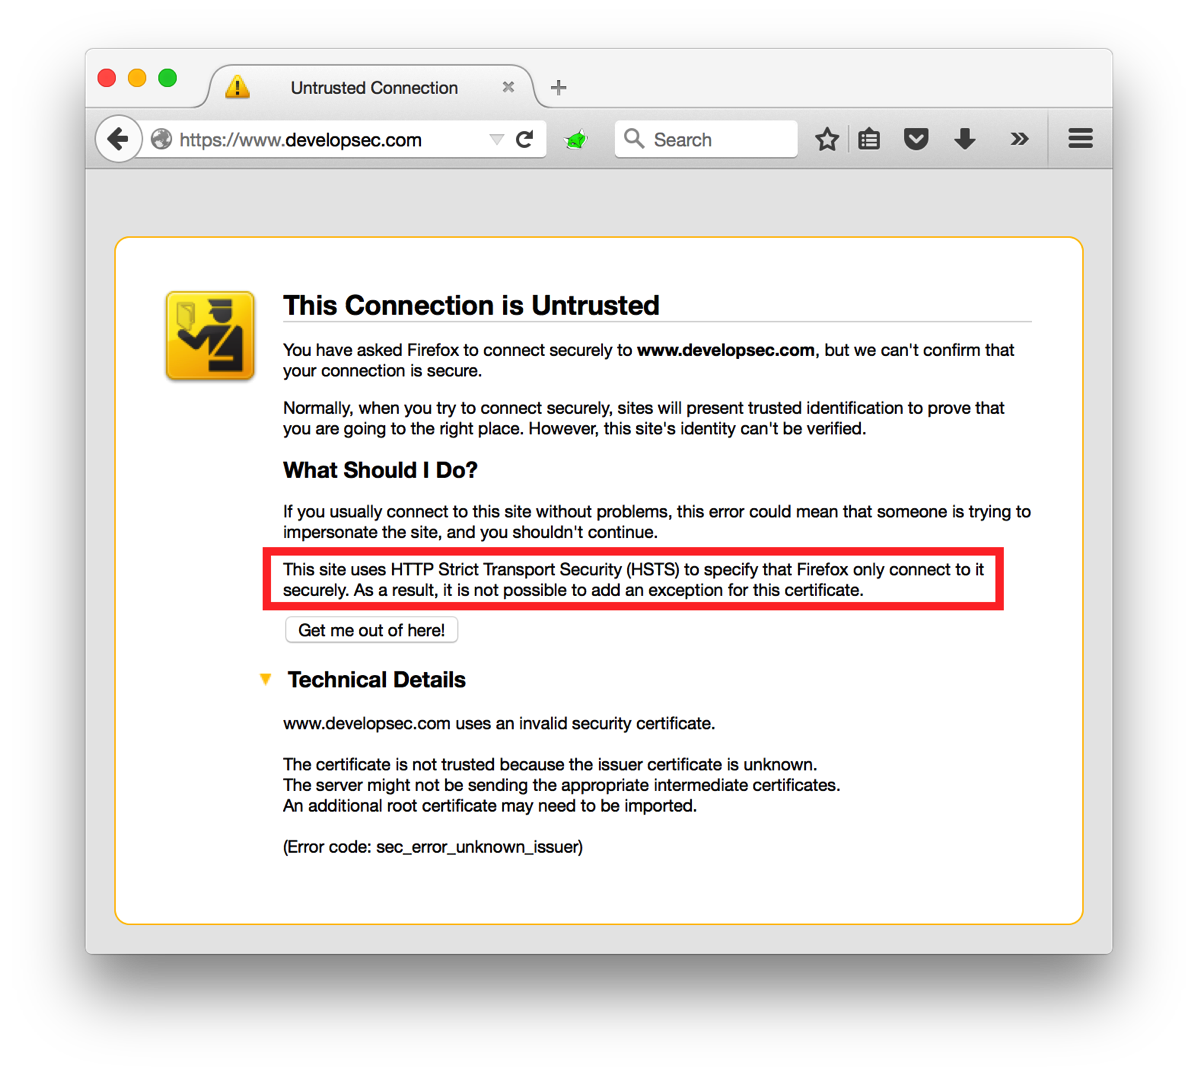
A while back I asked the question "Is HTTP being left behind for HTTPS?". If you are looking to make the move to an HTTPS only web space one of the settings you can configure is HTTP Strict Transport Security, or HSTS. The idea behind HSTS is that it will tell the browser to only communicate with the web site over a secure channel. Even if the user attempts to switch to HTTP, the browser will make the change before it even sends the request. HSTS is implemented as a response header with a … [Read more...] about HTTP Strict Transport Security (HSTS): Overview